
Andariel
Also tracked as Onyx SleetSilent ChollimaPLUTONIUMStoneflyDarkSeoulAPT45Jumpy Pisces
MITRE ATT&CK G0138
Andariel pays for its own espionage. A 2024 U.S. indictment describes ransomware against American hospitals and healthcare providers, with the proceeds funding intrusions into defence contractors, aerospace firms and energy and nuclear engineering organisations.
The victim list therefore looks unrelated, a hospital system and a nuclear engineering firm, and a sector lens will call the group unfocused. It is not: one set of victims pays for access to the other.
- Named individuals
- 1 profiled from law-enforcement records
- Fabricated personas
- None reconstructed under this tag
- Indicators
- 183 in the searchable index
- Hunts
- None in the hunt library
How it differs from the other clusters here
Other clusters keep money and intelligence separate; in Andariel a ransom note and the theft of engineering documentation belong to the same operation.
Initial access differs: the joint U.S. and allied advisory emphasises exploitation of known vulnerabilities in internet-facing systems, not persuading a person.
The exposure is a patch level, which changes who owns the risk and what a defender can do in advance.
Compare Lazarus GroupAPT38KimsukyRGB (Reconnaissance General Bureau)Remote Worker Fraud / Contagious InterviewAPT37KonniMoonstone SleetPolinRider
What a defender would see
For healthcare and critical-infrastructure operators, the sequence is ordinary: an unpatched internet-facing system, a web shell, then lateral movement with harvested credentials.
Nothing in it is DPRK-specific; the hygiene that stops a criminal ransomware affiliate stops this.
Staging of documents and engineering data before encryption is not incidental, since the intrusion is also a collection operation.
If ransomware hits a defence, aerospace, energy or nuclear supply-chain organisation, ask the exfiltration question independently of the ransom question.
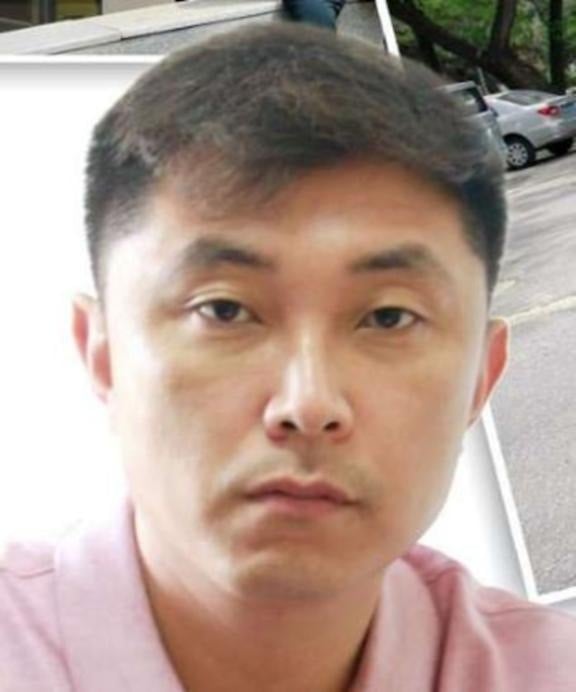
Named individuals
Every person below is named in a public charging document, sanctions record or law-enforcement wanted notice that carries this cluster tag. Each profile lists the records it draws on and nothing beyond them.
Indicators
The 183 indicators the index holds under this cluster. The complete index is on Remote Workers.
| Indicator | Type | Persona and cluster | Report date | Sources |
|---|
| Indicator | Type | Persona and cluster | Report date | Sources |
|---|---|---|---|---|
115.92.103.37 fixed line |
ip address MATCHED IN SOURCE | Andariel | 2017-12-07 | 2 |
144.208.127.115 data centre |
ip address MATCHED IN SOURCE | Andariel | 2024-10-02 | 1 |
172.96.137.224 data centre |
ip address MATCHED IN SOURCE | Andariel | 2024-10-02 | 3 |
216.120.201.112 data centre |
ip address MATCHED IN SOURCE | Andariel | 2024-10-02 | 1 |
217.195.153.209 data centre |
ip address MATCHED IN SOURCE | Andariel | 2024-10-02 | 1 |
22a279c5685d7c3e24c04580204a8a932b2909a77a549bdd7bcf7ead285efde9 |
file hash MATCHED IN SOURCE | Andariel | 2017-12-07 | 2 |
23.254.226.90 data centre |
ip address MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky Contagious Interview DPRK (cluster unattributed) | 2023-10-25 | 5 |
2360a69e5fd7217e977123c81d3dbb60bf4763a9dae6949bc1900234f7762df1 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky Contagious Interview | 2023-10-25 | 4 |
3ea2ead8f3cec030906dcbffe3efd5c5d77d5d375d4a54cca03bfe8a6cb59940 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky DPRK (cluster unattributed) | 2023-10-25 | 4 |
40.121.90.194 data centre |
ip address MATCHED IN SOURCE | Lazarus Group Andariel | 2022-09-08 | 3 |
485465f38582377f9496a6c77262670a313d8c6e01fd29a5dbd919b9a40e68d5 |
file hash MATCHED IN SOURCE | Andariel | 2024-10-02 | 1 |
49.239.189.45 fixed line |
ip address MATCHED IN SOURCE | Andariel | 2017-12-07 | 2 |
51.81.168.157 data centre |
ip address MATCHED IN SOURCE | Andariel | 2024-10-02 | 1 |
db6a9934570fa98a93a979e7e0e218e0c9710e5a787b18c6948f2eedd9338984 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2023-08-24 | 2 |
01b58f2ff2c14feed46a0768ea46686d |
file hash MATCHED IN SOURCE | Lazarus Group Andariel | 2026-08-03 | 2 |
07766e6e9d9f86775ad564a65af292c1 |
file hash MATCHED IN SOURCE | Lazarus Group Andariel | 2026-08-03 | 2 |
08e19a0d516d14e564359ee111ed2586 |
file hash MATCHED IN SOURCE | Lazarus Group Andariel | 2026-08-03 | 2 |
0d2e61c8a5e6280e065b61e75b848c68 |
file hash MATCHED IN SOURCE | Lazarus Group Andariel DPRK (cluster unattributed) | 2026-06-29 | 3 |
12391f66ee33d379108fd649a999e1a0 |
file hash MATCHED IN SOURCE | Lazarus Group Andariel DPRK (cluster unattributed) | 2026-06-24 | 4 |
hansom2008@protonmail.com |
email address MATCHED IN SOURCE | Lazarus Group Andariel | 2026-08-03 | 2 |
hansompay2008@yandex.com |
email address MATCHED IN SOURCE | Lazarus Group Andariel | 2026-08-03 | 2 |
15adac4d6fc1bddb0c940cdc0c6605b4 |
file hash MATCHED IN SOURCE | APT38 Andariel | 2026-05-21 | 1 |
53636c80d43a3c461dc8a3d2a2f2d4e1 |
file hash MATCHED IN SOURCE | APT38 Andariel | 2026-05-21 | 1 |
750173f1b36e502ff17e2c5eec03c602 |
file hash MATCHED IN SOURCE | APT38 Andariel | 2026-05-21 | 1 |
8edc77fb36bf80bb52d158cf9043cecd |
file hash MATCHED IN SOURCE | APT38 Andariel | 2026-05-21 | 1 |
b15a55f9a23998b1976622bd3b9a3ad9 |
file hash MATCHED IN SOURCE | APT38 Andariel | 2026-05-21 | 1 |
b500a8ffd4907a1dfda985683f1de1df |
file hash MATCHED IN SOURCE | Andariel Kimsuky | 2022-10-12 | 6 |
081804b491c70bfa63ecdbe9fd4618d3570706ad8b71dba13e234069648e5e48 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
0b5db31e47b0dccfdec46e74c0e70c6a1684768dbacc9eacbb4fd2ef851994c7 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
15d53bb839e00405a34a8b690ec181f5555fc4f891b8248ae7fa72bad28315a9 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
2546d239a262c24a6f8ea01d890cbc459a22db79b379b6ec3b24fbb56efb5381 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
3c8dbfcbb4fccbaf924f9a650a04cb4715f4a58d51ef49cc75bfcef0ac258a3e |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
479038eb12ed07893ee0dcc04fbdcf182489bbb271f5a4f90f83874881a80ce3 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
492a643bd1efdaca4ca125ade1b606e7bbf00e995ac9115ac84d1c4c59cb66dd |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
5009c7d1590c1f8c05827122172583ddf924c53b55a46826abf66da46725505a |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
5c907b722c53a5be256dc5f96b755bc9e0b032cc30973a52d984d4174bace456 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 3 |
5e40d106977017b1ed235419b1e59ff090e1f43ac57da1bb5d80d66ae53b1df8 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2021-02-17 | 4 |
63fb47c3b4693409ebadf8a5179141af5cf45a46d1e98e5f763ca0d7d64fb17c |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
689cfaa9319f3f7529a31472ecf6b2e0ca6891b736de009e0b6c2ebac958cc94 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
6c121f2b2efa6592c2c22b29218157ec9e63f385e7a1d7425857d603ddef8c59 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
7667d1b8fcc4f712084e3e3f8b4ab505ab150c52aea7b219249ec508b4b0e224 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
87c5d0c93b80acf61d24e7aaf0faae231ab507ca45483ad3d441b5d1acebc43c |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
8bfa4fe0534c0062393b6a2597c3491f7df3bf2eabfe06544c53bdf1f38db6d4 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
91eaf215be336eae983d069de16630cc3580e222c427f785e0da312d0692d0fd |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2021-04-15 | 4 |
927b3564c1cf884d2a05e1d7bd24362ce8563a1e9b85be776190ab7f8af192f6 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
973f7939ea03fd2c9663dafc21bb968f56ed1b9a56b0284acf73c3ee141c053c |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 3 |
99dbc6fe3c3e465052fcefa1642861747dc9e069eeb244589b605bd710b1e0d1 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
a03d13c9825e150810e6e6aaf053d71ec5a53b86581414dd982a74d4a8bc5475 |
file hash MATCHED IN SOURCE | Lazarus Group APT38 Andariel Kimsuky | 2024-09-09 | 2 |
20.20.100.32 data centre |
ip address MATCHED IN SOURCE | Andariel | 2024-12-22 | 2 |
3525a8a16ce8988885d435133b3e85d8 |
file hash MATCHED IN SOURCE | Andariel | 2024-12-22 | 2 |
Where the evidence comes from
Further reading
Published research on this cluster. None of it is this site’s work.
-
North Korea Cyber Group Conducts Global Espionage Campaign to Advance Regime's Military and Nuclear Programs (AA24-207A)
The joint advisory on this group, and the item to read first. It sets out the dual mission plainly and lists the initial-access vulnerabilities and post-exploitation behaviour the partner agencies observed.
-
North Korean Government Hacker Charged for Involvement in Ransomware Attacks Targeting U.S. Hospitals and Health Care Providers
The indictment of Rim Jong Hyok, published the same day as the advisory. This is where the funding relationship is stated as a charge: ransom proceeds paying for the infrastructure used against defence and energy targets.
-
Jumpy Pisces Engages in Play Ransomware
Unit 42's own name for this cluster, and a documented case — assessed with moderate confidence — of it collaborating with or acting as an affiliate of the criminal Play ransomware operation rather than deploying its own encryptor.