
Ming Cheng
Also reported as: hodlwarden0xcrypoopsNikolic Chiraghodl_warden
A fabricated professional identity used in the DPRK remote IT-worker scheme. Most of what follows is transcribed from the cited post, in which a named researcher attributes these accounts to a single operator, Ming Cheng. The attribution is theirs, not this site's.
The remainder was read by this site from the account itself and is cited to the page and date it was read.
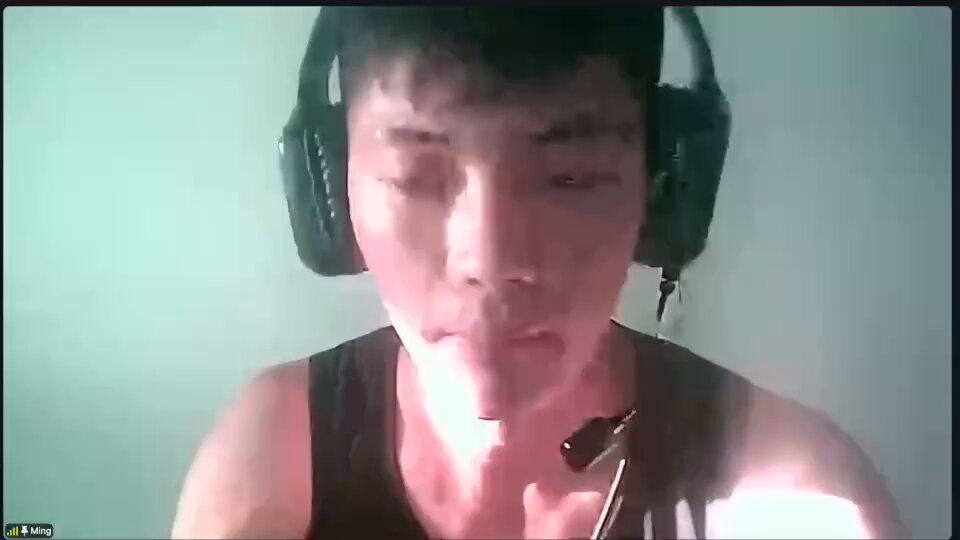
Still from a video call, captured during an interview; the call labels the participant Ming.
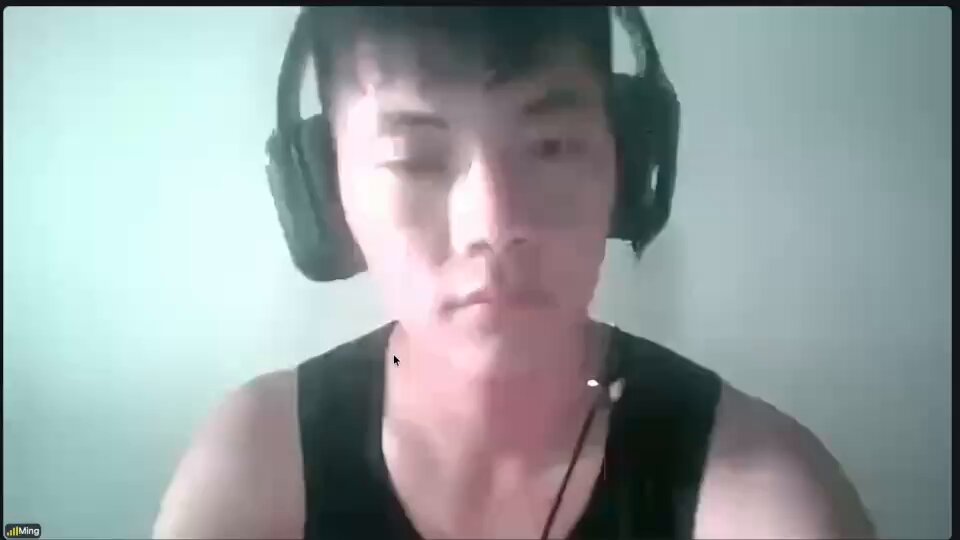
A second still from the same video call.
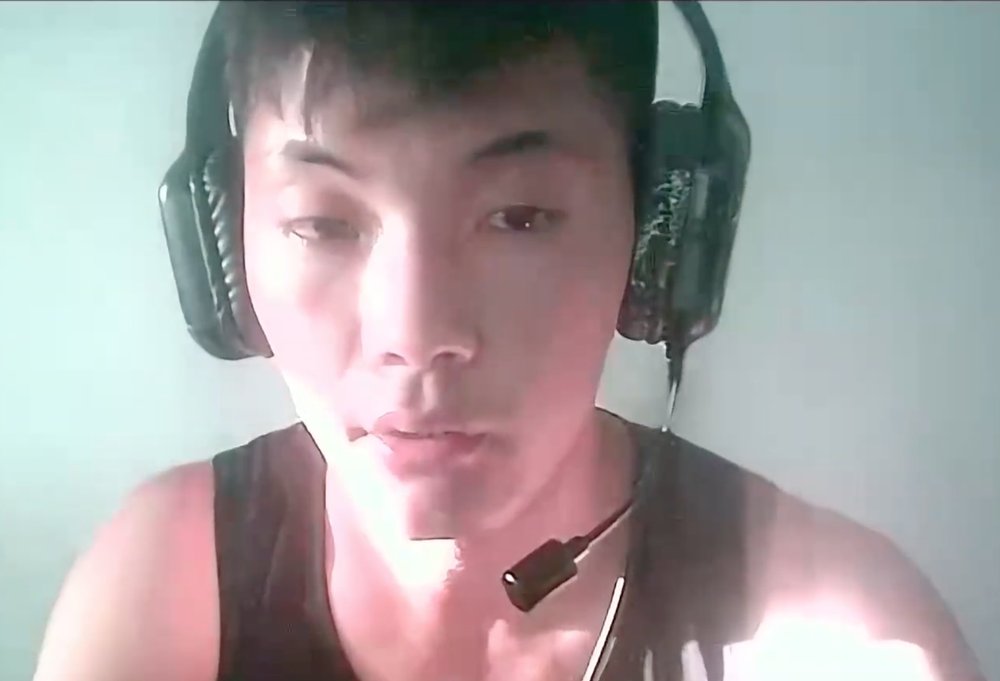
Photograph published by the registry under this persona, captioned there as “Ming Cheng on a video call.”. It shows whoever appeared under this identity, which is not necessarily the person whose details the identity was assembled from — these operations routinely build a persona around a real, uninvolved person.
Profiles and evidence
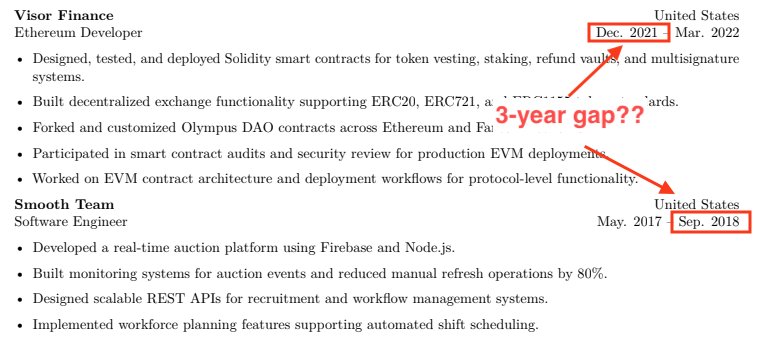
Resume excerpt the researcher annotated, flagging a three-year gap in the employment dates.
Files published with this identity
| File | Description | Size | Published by |
|---|---|---|---|
| ming_cheng_cv.pdf | Ming Cheng CV | 26 KB | Lazarus Group DPRK IT-Worker Registry (lazarus.group) |
Identifiers attributed to this persona
14 indicators the sources below record for this operator, each with its sources.
| Indicator | Type | Account status |
|---|---|---|
Ming Cheng |
alias | |
Nikolic Chirag |
alias | |
hodlwarden.com |
domain | |
hodlwarden@gmail.com |
email address | |
https://github.com/0xcrypoops |
github profile | removed |
https://github.com/crypdev007 |
github profile | live |
https://github.com/hodlwarden |
github profile | removed |
https://gitlab.com/hodlwarden |
gitlab account | live |
170.205.31.7 |
ip address | |
+17745166548 |
phone number | |
https://t.me/hodlwarden |
telegram account | live |
https://t.me/oxcrypoops |
telegram account | live |
https://x.com/0xcrypoops |
x account | |
https://x.com/hodlwarden |
x account |
Ming Cheng
alias IT Worker FraudContagious Interview CURATED
Sources
-
The researcher describes interviewing this identity as an applicant for a remote engineering role and assessing them as a North Korean IT worker. The account is presented under the name Ming Cheng. The thread notes a three-year gap in the resume covering 2018 to 2021, which the applicant explained as COVID-19 treatment beginning in 2019, months before the virus was known in China, and says the interview was cut short by a connection problem shortly after the applicant was asked whether he was North Korean. The third post of that thread publishes the whole application under the heading "all the fake details he applied with for anyone tracking", and is where the address, telephone number, GitHub, Telegram, IP address and website here come from. It was missed on the first pass: X renders a post that long behind a Show more control, and the syndication endpoint the reader uses returns it truncated and says so. It has to be read in a browser. That post also attributes the GitHub account to the Contagious Trader campaign, weaponised cryptocurrency trading bots, citing kmsec's write-up, which is already a source here; this entry carries that label alongside IT Worker Fraud because the researcher makes both claims. This is a second, independent researcher reaching the same conclusion about an identity the lazarus.group registry already records, so the account carries both citations. Two days after the thread that named this operator, the researcher reported that it had rotated to a new persona, 0xcrypoops, and gave the replacement X, GitHub and Telegram accounts. The three are recorded here rather than as a separate persona because the source states outright that they are the same operator continuing. Note that the Telegram handle for the replacement is not a copy of the other two: it begins with the letter o where the X and GitHub handles begin with a zero, and it is transcribed as the post links it.
x.com/tanuki42_/status/2088278343653413254 — tanuki42 (@tanuki42_) -
Entry in the lazarus.group DPRK IT-worker registry, which asserts that these accounts belong to one operator. The registry publishes no methodology, so this is recorded as its claim and not as a finding of this site. Its evidence links and its cross-references to other operators in the same registry are deliberately not reproduced as indicators.
lazarus.group/team/ming-cheng — Lazarus Group DPRK IT-Worker Registry (lazarus.group) -
Found on 12 September 2026 by probing the platforms an operator usually reuses a login on, for the handles this site already holds, and read directly from the page cited. A GitLab account under hodlwarden, one of the logins attributed to this operator, created on 9 April 2026 — months after the reporting that named the handle, which makes it the only account here the operator is known to have opened since being written about. It displays "Hodl Warden", which is the handle spaced out rather than a name, and carries no bio, location or links.
gitlab.com/hodlwarden — Chollima Hunter -
Found on 24 September 2026 by searching GitHub's commit index for published persona addresses and reading which account GitHub attributes the commits to. GitHub credits a commit to the account that has the signing address registered and verified, which only the holder of the mailbox can do, so an attributed account is one the address's holder controls, whichever repository the commits sit in and whenever the address was added. Counts are of the commits GitHub's search returns, up to 100. GitHub attributes 63 commits signed hodlwarden@gmail.com, an address the lazarus.group registry publishes for this persona, to github.com/crypdev007, account id 37245718, created on 10 March 2018, display name crypdev007, with 74 public repositories.
github.com/crypdev007 — Chollima Hunter
Nikolic Chirag
alias IT Worker FraudContagious Interview RESEARCHER POST
Sources
-
The researcher describes interviewing this identity as an applicant for a remote engineering role and assessing them as a North Korean IT worker. The account is presented under the name Ming Cheng. The thread notes a three-year gap in the resume covering 2018 to 2021, which the applicant explained as COVID-19 treatment beginning in 2019, months before the virus was known in China, and says the interview was cut short by a connection problem shortly after the applicant was asked whether he was North Korean. The third post of that thread publishes the whole application under the heading "all the fake details he applied with for anyone tracking", and is where the address, telephone number, GitHub, Telegram, IP address and website here come from. It was missed on the first pass: X renders a post that long behind a Show more control, and the syndication endpoint the reader uses returns it truncated and says so. It has to be read in a browser. That post also attributes the GitHub account to the Contagious Trader campaign, weaponised cryptocurrency trading bots, citing kmsec's write-up, which is already a source here; this entry carries that label alongside IT Worker Fraud because the researcher makes both claims. This is a second, independent researcher reaching the same conclusion about an identity the lazarus.group registry already records, so the account carries both citations. Two days after the thread that named this operator, the researcher reported that it had rotated to a new persona, 0xcrypoops, and gave the replacement X, GitHub and Telegram accounts. The three are recorded here rather than as a separate persona because the source states outright that they are the same operator continuing. Note that the Telegram handle for the replacement is not a copy of the other two: it begins with the letter o where the X and GitHub handles begin with a zero, and it is transcribed as the post links it.
x.com/tanuki42_/status/2088278343653413254 — tanuki42 (@tanuki42_) -
Entry in the lazarus.group DPRK IT-worker registry, which asserts that these accounts belong to one operator. The registry publishes no methodology, so this is recorded as its claim and not as a finding of this site. Its evidence links and its cross-references to other operators in the same registry are deliberately not reproduced as indicators.
lazarus.group/team/ming-cheng — Lazarus Group DPRK IT-Worker Registry (lazarus.group)
hodlwarden.com
domain IT Worker FraudContagious Interview RESEARCHER POST
Registration
| Registered | 2026-03-07 |
|---|---|
| Registrar | HOSTINGER operations, UAB |
| Expires | 2027-03-07 |
| Last changed | 2026-03-07 |
| Status | client transfer prohibited |
Source
-
The researcher describes interviewing this identity as an applicant for a remote engineering role and assessing them as a North Korean IT worker. The account is presented under the name Ming Cheng. The thread notes a three-year gap in the resume covering 2018 to 2021, which the applicant explained as COVID-19 treatment beginning in 2019, months before the virus was known in China, and says the interview was cut short by a connection problem shortly after the applicant was asked whether he was North Korean. The third post of that thread publishes the whole application under the heading "all the fake details he applied with for anyone tracking", and is where the address, telephone number, GitHub, Telegram, IP address and website here come from. It was missed on the first pass: X renders a post that long behind a Show more control, and the syndication endpoint the reader uses returns it truncated and says so. It has to be read in a browser. That post also attributes the GitHub account to the Contagious Trader campaign, weaponised cryptocurrency trading bots, citing kmsec's write-up, which is already a source here; this entry carries that label alongside IT Worker Fraud because the researcher makes both claims. This is a second, independent researcher reaching the same conclusion about an identity the lazarus.group registry already records, so the account carries both citations. Two days after the thread that named this operator, the researcher reported that it had rotated to a new persona, 0xcrypoops, and gave the replacement X, GitHub and Telegram accounts. The three are recorded here rather than as a separate persona because the source states outright that they are the same operator continuing. Note that the Telegram handle for the replacement is not a copy of the other two: it begins with the letter o where the X and GitHub handles begin with a zero, and it is transcribed as the post links it.
x.com/tanuki42_/status/2088278349487759785 — tanuki42 (@tanuki42_)
hodlwarden@gmail.com
email address IT Worker FraudContagious Interview CURATED
Sources
-
The researcher describes interviewing this identity as an applicant for a remote engineering role and assessing them as a North Korean IT worker. The account is presented under the name Ming Cheng. The thread notes a three-year gap in the resume covering 2018 to 2021, which the applicant explained as COVID-19 treatment beginning in 2019, months before the virus was known in China, and says the interview was cut short by a connection problem shortly after the applicant was asked whether he was North Korean. The third post of that thread publishes the whole application under the heading "all the fake details he applied with for anyone tracking", and is where the address, telephone number, GitHub, Telegram, IP address and website here come from. It was missed on the first pass: X renders a post that long behind a Show more control, and the syndication endpoint the reader uses returns it truncated and says so. It has to be read in a browser. That post also attributes the GitHub account to the Contagious Trader campaign, weaponised cryptocurrency trading bots, citing kmsec's write-up, which is already a source here; this entry carries that label alongside IT Worker Fraud because the researcher makes both claims. This is a second, independent researcher reaching the same conclusion about an identity the lazarus.group registry already records, so the account carries both citations. Two days after the thread that named this operator, the researcher reported that it had rotated to a new persona, 0xcrypoops, and gave the replacement X, GitHub and Telegram accounts. The three are recorded here rather than as a separate persona because the source states outright that they are the same operator continuing. Note that the Telegram handle for the replacement is not a copy of the other two: it begins with the letter o where the X and GitHub handles begin with a zero, and it is transcribed as the post links it.
x.com/tanuki42_/status/2088278349487759785 — tanuki42 (@tanuki42_) -
Entry in the lazarus.group DPRK IT-worker registry, which asserts that these accounts belong to one operator. The registry publishes no methodology, so this is recorded as its claim and not as a finding of this site. Its evidence links and its cross-references to other operators in the same registry are deliberately not reproduced as indicators.
lazarus.group/team/ming-cheng — Lazarus Group DPRK IT-Worker Registry (lazarus.group) -
Found on 24 September 2026 by searching GitHub's commit index for published persona addresses and reading which account GitHub attributes the commits to. GitHub credits a commit to the account that has the signing address registered and verified, which only the holder of the mailbox can do, so an attributed account is one the address's holder controls, whichever repository the commits sit in and whenever the address was added. Counts are of the commits GitHub's search returns, up to 100. GitHub attributes 63 commits signed hodlwarden@gmail.com, an address the lazarus.group registry publishes for this persona, to github.com/crypdev007, account id 37245718, created on 10 March 2018, display name crypdev007, with 74 public repositories.
github.com/crypdev007 — Chollima Hunter
https://github.com/0xcrypoops
github profile IT Worker FraudContagious Interview RESEARCHER POST removed
removed
Source
-
The researcher describes interviewing this identity as an applicant for a remote engineering role and assessing them as a North Korean IT worker. The account is presented under the name Ming Cheng. The thread notes a three-year gap in the resume covering 2018 to 2021, which the applicant explained as COVID-19 treatment beginning in 2019, months before the virus was known in China, and says the interview was cut short by a connection problem shortly after the applicant was asked whether he was North Korean. The third post of that thread publishes the whole application under the heading "all the fake details he applied with for anyone tracking", and is where the address, telephone number, GitHub, Telegram, IP address and website here come from. It was missed on the first pass: X renders a post that long behind a Show more control, and the syndication endpoint the reader uses returns it truncated and says so. It has to be read in a browser. That post also attributes the GitHub account to the Contagious Trader campaign, weaponised cryptocurrency trading bots, citing kmsec's write-up, which is already a source here; this entry carries that label alongside IT Worker Fraud because the researcher makes both claims. This is a second, independent researcher reaching the same conclusion about an identity the lazarus.group registry already records, so the account carries both citations. Two days after the thread that named this operator, the researcher reported that it had rotated to a new persona, 0xcrypoops, and gave the replacement X, GitHub and Telegram accounts. The three are recorded here rather than as a separate persona because the source states outright that they are the same operator continuing. Note that the Telegram handle for the replacement is not a copy of the other two: it begins with the letter o where the X and GitHub handles begin with a zero, and it is transcribed as the post links it.
x.com/tanuki42_/status/2088839296518164599 — tanuki42 (@tanuki42_)
https://github.com/crypdev007
github profile IT Worker Fraud CURATED live
live
Source
-
Found on 24 September 2026 by searching GitHub's commit index for published persona addresses and reading which account GitHub attributes the commits to. GitHub credits a commit to the account that has the signing address registered and verified, which only the holder of the mailbox can do, so an attributed account is one the address's holder controls, whichever repository the commits sit in and whenever the address was added. Counts are of the commits GitHub's search returns, up to 100. GitHub attributes 63 commits signed hodlwarden@gmail.com, an address the lazarus.group registry publishes for this persona, to github.com/crypdev007, account id 37245718, created on 10 March 2018, display name crypdev007, with 74 public repositories.
github.com/crypdev007 — Chollima Hunter
https://github.com/hodlwarden
github profile IT Worker FraudContagious Interview RESEARCHER POST removed
removed
Sources
-
The researcher describes interviewing this identity as an applicant for a remote engineering role and assessing them as a North Korean IT worker. The account is presented under the name Ming Cheng. The thread notes a three-year gap in the resume covering 2018 to 2021, which the applicant explained as COVID-19 treatment beginning in 2019, months before the virus was known in China, and says the interview was cut short by a connection problem shortly after the applicant was asked whether he was North Korean. The third post of that thread publishes the whole application under the heading "all the fake details he applied with for anyone tracking", and is where the address, telephone number, GitHub, Telegram, IP address and website here come from. It was missed on the first pass: X renders a post that long behind a Show more control, and the syndication endpoint the reader uses returns it truncated and says so. It has to be read in a browser. That post also attributes the GitHub account to the Contagious Trader campaign, weaponised cryptocurrency trading bots, citing kmsec's write-up, which is already a source here; this entry carries that label alongside IT Worker Fraud because the researcher makes both claims. This is a second, independent researcher reaching the same conclusion about an identity the lazarus.group registry already records, so the account carries both citations. Two days after the thread that named this operator, the researcher reported that it had rotated to a new persona, 0xcrypoops, and gave the replacement X, GitHub and Telegram accounts. The three are recorded here rather than as a separate persona because the source states outright that they are the same operator continuing. Note that the Telegram handle for the replacement is not a copy of the other two: it begins with the letter o where the X and GitHub handles begin with a zero, and it is transcribed as the post links it.
x.com/tanuki42_/status/2088278349487759785 — tanuki42 (@tanuki42_) -
Entry in the lazarus.group DPRK IT-worker registry, which asserts that these accounts belong to one operator. The registry publishes no methodology, so this is recorded as its claim and not as a finding of this site. Its evidence links and its cross-references to other operators in the same registry are deliberately not reproduced as indicators.
lazarus.group/team/ming-cheng — Lazarus Group DPRK IT-Worker Registry (lazarus.group)
https://gitlab.com/hodlwarden
gitlab account IT Worker Fraud CURATED live
live
Source
-
Found on 12 September 2026 by probing the platforms an operator usually reuses a login on, for the handles this site already holds, and read directly from the page cited. A GitLab account under hodlwarden, one of the logins attributed to this operator, created on 9 April 2026 — months after the reporting that named the handle, which makes it the only account here the operator is known to have opened since being written about. It displays "Hodl Warden", which is the handle spaced out rather than a name, and carries no bio, location or links.
gitlab.com/hodlwarden — Chollima Hunter
170.205.31.7
ip address IT Worker FraudContagious Interview RESEARCHER POST
Network
| Kind | data centre |
|---|---|
| Network | Advin Services LLC |
| Announced by | AS206216 Advin Services LLC |
| Country | United States |
| Flags | hosting range |
Source
-
The researcher describes interviewing this identity as an applicant for a remote engineering role and assessing them as a North Korean IT worker. The account is presented under the name Ming Cheng. The thread notes a three-year gap in the resume covering 2018 to 2021, which the applicant explained as COVID-19 treatment beginning in 2019, months before the virus was known in China, and says the interview was cut short by a connection problem shortly after the applicant was asked whether he was North Korean. The third post of that thread publishes the whole application under the heading "all the fake details he applied with for anyone tracking", and is where the address, telephone number, GitHub, Telegram, IP address and website here come from. It was missed on the first pass: X renders a post that long behind a Show more control, and the syndication endpoint the reader uses returns it truncated and says so. It has to be read in a browser. That post also attributes the GitHub account to the Contagious Trader campaign, weaponised cryptocurrency trading bots, citing kmsec's write-up, which is already a source here; this entry carries that label alongside IT Worker Fraud because the researcher makes both claims. This is a second, independent researcher reaching the same conclusion about an identity the lazarus.group registry already records, so the account carries both citations. Two days after the thread that named this operator, the researcher reported that it had rotated to a new persona, 0xcrypoops, and gave the replacement X, GitHub and Telegram accounts. The three are recorded here rather than as a separate persona because the source states outright that they are the same operator continuing. Note that the Telegram handle for the replacement is not a copy of the other two: it begins with the letter o where the X and GitHub handles begin with a zero, and it is transcribed as the post links it.
x.com/tanuki42_/status/2088278349487759785 — tanuki42 (@tanuki42_)
+17745166548
phone number IT Worker FraudContagious Interview RESEARCHER POST
Line type
| Line type | Wireless |
|---|---|
| Carrier | SINCH |
| Rate centre | EAST BRIDGEWATER, MA |
Sources
-
The researcher describes interviewing this identity as an applicant for a remote engineering role and assessing them as a North Korean IT worker. The account is presented under the name Ming Cheng. The thread notes a three-year gap in the resume covering 2018 to 2021, which the applicant explained as COVID-19 treatment beginning in 2019, months before the virus was known in China, and says the interview was cut short by a connection problem shortly after the applicant was asked whether he was North Korean. The third post of that thread publishes the whole application under the heading "all the fake details he applied with for anyone tracking", and is where the address, telephone number, GitHub, Telegram, IP address and website here come from. It was missed on the first pass: X renders a post that long behind a Show more control, and the syndication endpoint the reader uses returns it truncated and says so. It has to be read in a browser. That post also attributes the GitHub account to the Contagious Trader campaign, weaponised cryptocurrency trading bots, citing kmsec's write-up, which is already a source here; this entry carries that label alongside IT Worker Fraud because the researcher makes both claims. This is a second, independent researcher reaching the same conclusion about an identity the lazarus.group registry already records, so the account carries both citations. Two days after the thread that named this operator, the researcher reported that it had rotated to a new persona, 0xcrypoops, and gave the replacement X, GitHub and Telegram accounts. The three are recorded here rather than as a separate persona because the source states outright that they are the same operator continuing. Note that the Telegram handle for the replacement is not a copy of the other two: it begins with the letter o where the X and GitHub handles begin with a zero, and it is transcribed as the post links it.
x.com/tanuki42_/status/2088278349487759785 — tanuki42 (@tanuki42_) -
Entry in the lazarus.group DPRK IT-worker registry, which asserts that these accounts belong to one operator. The registry publishes no methodology, so this is recorded as its claim and not as a finding of this site. Its evidence links and its cross-references to other operators in the same registry are deliberately not reproduced as indicators.
lazarus.group/team/ming-cheng — Lazarus Group DPRK IT-Worker Registry (lazarus.group)
https://t.me/hodlwarden
telegram account IT Worker FraudContagious Interview RESEARCHER POST live
live
Sources
-
The researcher describes interviewing this identity as an applicant for a remote engineering role and assessing them as a North Korean IT worker. The account is presented under the name Ming Cheng. The thread notes a three-year gap in the resume covering 2018 to 2021, which the applicant explained as COVID-19 treatment beginning in 2019, months before the virus was known in China, and says the interview was cut short by a connection problem shortly after the applicant was asked whether he was North Korean. The third post of that thread publishes the whole application under the heading "all the fake details he applied with for anyone tracking", and is where the address, telephone number, GitHub, Telegram, IP address and website here come from. It was missed on the first pass: X renders a post that long behind a Show more control, and the syndication endpoint the reader uses returns it truncated and says so. It has to be read in a browser. That post also attributes the GitHub account to the Contagious Trader campaign, weaponised cryptocurrency trading bots, citing kmsec's write-up, which is already a source here; this entry carries that label alongside IT Worker Fraud because the researcher makes both claims. This is a second, independent researcher reaching the same conclusion about an identity the lazarus.group registry already records, so the account carries both citations. Two days after the thread that named this operator, the researcher reported that it had rotated to a new persona, 0xcrypoops, and gave the replacement X, GitHub and Telegram accounts. The three are recorded here rather than as a separate persona because the source states outright that they are the same operator continuing. Note that the Telegram handle for the replacement is not a copy of the other two: it begins with the letter o where the X and GitHub handles begin with a zero, and it is transcribed as the post links it.
x.com/tanuki42_/status/2088278349487759785 — tanuki42 (@tanuki42_) -
Entry in the lazarus.group DPRK IT-worker registry, which asserts that these accounts belong to one operator. The registry publishes no methodology, so this is recorded as its claim and not as a finding of this site. Its evidence links and its cross-references to other operators in the same registry are deliberately not reproduced as indicators.
lazarus.group/team/ming-cheng — Lazarus Group DPRK IT-Worker Registry (lazarus.group)
https://t.me/oxcrypoops
telegram account IT Worker FraudContagious Interview RESEARCHER POST live
live
Source
-
The researcher describes interviewing this identity as an applicant for a remote engineering role and assessing them as a North Korean IT worker. The account is presented under the name Ming Cheng. The thread notes a three-year gap in the resume covering 2018 to 2021, which the applicant explained as COVID-19 treatment beginning in 2019, months before the virus was known in China, and says the interview was cut short by a connection problem shortly after the applicant was asked whether he was North Korean. The third post of that thread publishes the whole application under the heading "all the fake details he applied with for anyone tracking", and is where the address, telephone number, GitHub, Telegram, IP address and website here come from. It was missed on the first pass: X renders a post that long behind a Show more control, and the syndication endpoint the reader uses returns it truncated and says so. It has to be read in a browser. That post also attributes the GitHub account to the Contagious Trader campaign, weaponised cryptocurrency trading bots, citing kmsec's write-up, which is already a source here; this entry carries that label alongside IT Worker Fraud because the researcher makes both claims. This is a second, independent researcher reaching the same conclusion about an identity the lazarus.group registry already records, so the account carries both citations. Two days after the thread that named this operator, the researcher reported that it had rotated to a new persona, 0xcrypoops, and gave the replacement X, GitHub and Telegram accounts. The three are recorded here rather than as a separate persona because the source states outright that they are the same operator continuing. Note that the Telegram handle for the replacement is not a copy of the other two: it begins with the letter o where the X and GitHub handles begin with a zero, and it is transcribed as the post links it.
x.com/tanuki42_/status/2088839296518164599 — tanuki42 (@tanuki42_)
https://x.com/0xcrypoops
x account IT Worker FraudContagious Interview RESEARCHER POST
Source
-
The researcher describes interviewing this identity as an applicant for a remote engineering role and assessing them as a North Korean IT worker. The account is presented under the name Ming Cheng. The thread notes a three-year gap in the resume covering 2018 to 2021, which the applicant explained as COVID-19 treatment beginning in 2019, months before the virus was known in China, and says the interview was cut short by a connection problem shortly after the applicant was asked whether he was North Korean. The third post of that thread publishes the whole application under the heading "all the fake details he applied with for anyone tracking", and is where the address, telephone number, GitHub, Telegram, IP address and website here come from. It was missed on the first pass: X renders a post that long behind a Show more control, and the syndication endpoint the reader uses returns it truncated and says so. It has to be read in a browser. That post also attributes the GitHub account to the Contagious Trader campaign, weaponised cryptocurrency trading bots, citing kmsec's write-up, which is already a source here; this entry carries that label alongside IT Worker Fraud because the researcher makes both claims. This is a second, independent researcher reaching the same conclusion about an identity the lazarus.group registry already records, so the account carries both citations. Two days after the thread that named this operator, the researcher reported that it had rotated to a new persona, 0xcrypoops, and gave the replacement X, GitHub and Telegram accounts. The three are recorded here rather than as a separate persona because the source states outright that they are the same operator continuing. Note that the Telegram handle for the replacement is not a copy of the other two: it begins with the letter o where the X and GitHub handles begin with a zero, and it is transcribed as the post links it.
x.com/tanuki42_/status/2088839296518164599 — tanuki42 (@tanuki42_)
https://x.com/hodlwarden
x account IT Worker FraudContagious Interview RESEARCHER POST
Sources
-
The researcher describes interviewing this identity as an applicant for a remote engineering role and assessing them as a North Korean IT worker. The account is presented under the name Ming Cheng. The thread notes a three-year gap in the resume covering 2018 to 2021, which the applicant explained as COVID-19 treatment beginning in 2019, months before the virus was known in China, and says the interview was cut short by a connection problem shortly after the applicant was asked whether he was North Korean. The third post of that thread publishes the whole application under the heading "all the fake details he applied with for anyone tracking", and is where the address, telephone number, GitHub, Telegram, IP address and website here come from. It was missed on the first pass: X renders a post that long behind a Show more control, and the syndication endpoint the reader uses returns it truncated and says so. It has to be read in a browser. That post also attributes the GitHub account to the Contagious Trader campaign, weaponised cryptocurrency trading bots, citing kmsec's write-up, which is already a source here; this entry carries that label alongside IT Worker Fraud because the researcher makes both claims. This is a second, independent researcher reaching the same conclusion about an identity the lazarus.group registry already records, so the account carries both citations. Two days after the thread that named this operator, the researcher reported that it had rotated to a new persona, 0xcrypoops, and gave the replacement X, GitHub and Telegram accounts. The three are recorded here rather than as a separate persona because the source states outright that they are the same operator continuing. Note that the Telegram handle for the replacement is not a copy of the other two: it begins with the letter o where the X and GitHub handles begin with a zero, and it is transcribed as the post links it.
x.com/tanuki42_/status/2088278343653413254 — tanuki42 (@tanuki42_) -
Entry in the lazarus.group DPRK IT-worker registry, which asserts that these accounts belong to one operator. The registry publishes no methodology, so this is recorded as its claim and not as a finding of this site. Its evidence links and its cross-references to other operators in the same registry are deliberately not reproduced as indicators.
lazarus.group/team/ming-cheng — Lazarus Group DPRK IT-Worker Registry (lazarus.group)
Sources
- x.com/tanuki42_/status/2088278343653413254 — tanuki42 (@tanuki42_)
- x.com/tanuki42_/status/2088839296518164599 — tanuki42 (@tanuki42_)
- x.com/tanuki42_/status/2088278349487759785 — tanuki42 (@tanuki42_)
- lazarus.group/team/ming-cheng — Lazarus Group DPRK IT-Worker Registry (lazarus.group)
- gitlab.com/hodlwarden — Chollima Hunter
- github.com/crypdev007 — Chollima Hunter