
Gerardo Salgado
Also reported as: Tammy Hans
A fabricated professional identity used in the DPRK remote IT-worker scheme. Most of what follows is transcribed from the cited post, in which a named researcher attributes these accounts to a single operator, Gerardo Salgado. The attribution is theirs, not this site's.
The remainder was read by this site from the account itself and is cited to the page and date it was read.
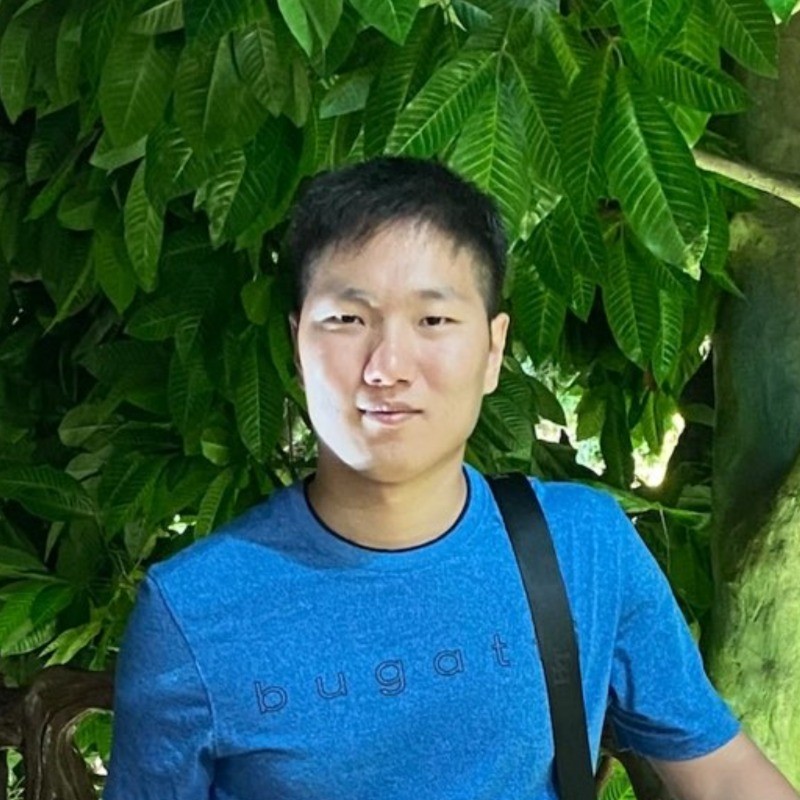
Photograph published in the cited post of the person appearing under the Gerardo Salgado identity. It shows whoever appeared under the identity, not necessarily the operator.
Identifiers attributed to this persona
23 indicators the sources below record for this operator, each with its sources.
| Indicator | Type | Account status |
|---|---|---|
Gerardo Salgado |
alias | |
Tammy Hans |
alias | |
alexgarayev018@gmail.com |
email address | |
alixrutherford20@gmail.com |
email address | |
ariyevrafael89@gmail.com |
email address | |
bobkovldmr@gmail.com |
email address | |
codejoshua018@gmail.com |
email address | |
courtneyastorga004@gmail.com |
email address | |
dev@ninjadevllc.com |
email address | |
dragonfire0827@gmail.com |
email address | |
financial@ninjadevllc.com |
email address | |
guoqiangzhangwork@gmail.com |
email address | |
jk6555838@gmail.com |
email address | |
mobileking0827@gmail.com |
email address | |
sojoshwork@gmail.com |
email address | |
techbizgo@protonmail.com |
email address | |
uiuxdesign721@gmail.com |
email address | |
volodymyr.bobkowork@outlook.com |
email address | |
zhangleowork@gmail.com |
email address | |
https://facebook.com/profile.php?id=100070818228999 |
facebook account | |
https://github.com/devvenom11 |
github profile | live |
37.200.77.102 |
ip address | |
45.43.135.155 |
ip address |
Gerardo Salgado
alias IT Worker Fraud CURATED
Sources
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853883109974022 — Narcass3 (@Narcass3) -
Found on 24 September 2026 by searching GitHub's commit index for published persona addresses and reading which account GitHub attributes the commits to. GitHub credits a commit to the account that has the signing address registered and verified, which only the holder of the mailbox can do, so an attributed account is one the address's holder controls, whichever repository the commits sit in and whenever the address was added. Counts are of the commits GitHub's search returns, up to 100. GitHub attributes 3 commits signed dragonfire.0827@gmail.com, an address Narcass3 publishes for this persona, and 13 commits signed zhangleowork@gmail.com, an address Narcass3 publishes for this persona, to github.com/devvenom11, account id 33862227, created on 21 November 2017, display name Leo Zhang, with 29 public repositories.
github.com/devvenom11 — Chollima Hunter
Tammy Hans
alias IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853883109974022 — Narcass3 (@Narcass3)
alexgarayev018@gmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853888193495143 — Narcass3 (@Narcass3)
alixrutherford20@gmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853890311610799 — Narcass3 (@Narcass3)
ariyevrafael89@gmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853890311610799 — Narcass3 (@Narcass3)
bobkovldmr@gmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853890311610799 — Narcass3 (@Narcass3)
codejoshua018@gmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853888193495143 — Narcass3 (@Narcass3)
courtneyastorga004@gmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853890311610799 — Narcass3 (@Narcass3)
dev@ninjadevllc.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853890311610799 — Narcass3 (@Narcass3)
dragonfire0827@gmail.com
email address IT Worker Fraud CURATED
Sources
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853888193495143 — Narcass3 (@Narcass3) -
Found on 24 September 2026 by searching GitHub's commit index for published persona addresses and reading which account GitHub attributes the commits to. GitHub credits a commit to the account that has the signing address registered and verified, which only the holder of the mailbox can do, so an attributed account is one the address's holder controls, whichever repository the commits sit in and whenever the address was added. Counts are of the commits GitHub's search returns, up to 100. GitHub attributes 3 commits signed dragonfire.0827@gmail.com, an address Narcass3 publishes for this persona, and 13 commits signed zhangleowork@gmail.com, an address Narcass3 publishes for this persona, to github.com/devvenom11, account id 33862227, created on 21 November 2017, display name Leo Zhang, with 29 public repositories.
github.com/devvenom11 — Chollima Hunter
financial@ninjadevllc.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853890311610799 — Narcass3 (@Narcass3)
guoqiangzhangwork@gmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853888193495143 — Narcass3 (@Narcass3)
jk6555838@gmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853890311610799 — Narcass3 (@Narcass3)
mobileking0827@gmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853888193495143 — Narcass3 (@Narcass3)
sojoshwork@gmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853890311610799 — Narcass3 (@Narcass3)
techbizgo@protonmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853888193495143 — Narcass3 (@Narcass3)
uiuxdesign721@gmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853890311610799 — Narcass3 (@Narcass3)
volodymyr.bobkowork@outlook.com
email address IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853890311610799 — Narcass3 (@Narcass3)
zhangleowork@gmail.com
email address IT Worker Fraud CURATED
Sources
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853888193495143 — Narcass3 (@Narcass3) -
Found on 24 September 2026 by searching GitHub's commit index for published persona addresses and reading which account GitHub attributes the commits to. GitHub credits a commit to the account that has the signing address registered and verified, which only the holder of the mailbox can do, so an attributed account is one the address's holder controls, whichever repository the commits sit in and whenever the address was added. Counts are of the commits GitHub's search returns, up to 100. GitHub attributes 3 commits signed dragonfire.0827@gmail.com, an address Narcass3 publishes for this persona, and 13 commits signed zhangleowork@gmail.com, an address Narcass3 publishes for this persona, to github.com/devvenom11, account id 33862227, created on 21 November 2017, display name Leo Zhang, with 29 public repositories.
github.com/devvenom11 — Chollima Hunter
https://facebook.com/profile.php?id=100070818228999
facebook account IT Worker Fraud RESEARCHER POST
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853883109974022 — Narcass3 (@Narcass3)
https://github.com/devvenom11
github profile IT Worker Fraud CURATED live
live
Source
-
Found on 24 September 2026 by searching GitHub's commit index for published persona addresses and reading which account GitHub attributes the commits to. GitHub credits a commit to the account that has the signing address registered and verified, which only the holder of the mailbox can do, so an attributed account is one the address's holder controls, whichever repository the commits sit in and whenever the address was added. Counts are of the commits GitHub's search returns, up to 100. GitHub attributes 3 commits signed dragonfire.0827@gmail.com, an address Narcass3 publishes for this persona, and 13 commits signed zhangleowork@gmail.com, an address Narcass3 publishes for this persona, to github.com/devvenom11, account id 33862227, created on 21 November 2017, display name Leo Zhang, with 29 public repositories.
github.com/devvenom11 — Chollima Hunter
37.200.77.102
ip address IT Worker Fraud RESEARCHER POST
Network
| Kind | fixed line |
|---|---|
| Network | ISP Podryad Nets |
| Announced by | AS196949 Natalia Sergeevna Filicheva |
| Country | Russia |
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853892056412538 — Narcass3 (@Narcass3)
45.43.135.155
ip address IT Worker Fraud RESEARCHER POST
Network
| Kind | data centre |
|---|---|
| Network | H4Y |
| Announced by | AS397373 H4Y Technologies LLC |
| Country | United States |
| Flags | hosting range |
Source
-
A five-post thread. The researcher states this operator infected his own machine with Contagious Interview malware, which is how the material became visible, and that he holds a large number of compromised accounts and has run two fake companies in the United States. The first of those, TechBizGo, was used to recruit facilitators through a neighbourhood listings page for Ogden, Utah; the second, Ninja Development LLC, advertised web3 and smart-contract development. The addresses in the third post are the ones the researcher says were most used; the fourth post continues the same list. The closing post of the thread, missed when this entry was first transcribed, carries two IP addresses tied to the operator; they are added here.
x.com/Narcass3/status/1955853892056412538 — Narcass3 (@Narcass3)
Sources
- x.com/Narcass3/status/1955853888193495143 — Narcass3 (@Narcass3)
- x.com/Narcass3/status/1955853890311610799 — Narcass3 (@Narcass3)
- x.com/Narcass3/status/1955853892056412538 — Narcass3 (@Narcass3)
- x.com/Narcass3/status/1955853883109974022 — Narcass3 (@Narcass3)
- github.com/devvenom11 — Chollima Hunter