
Evan Jones
Also reported as: Yucob Yun
A fabricated professional identity used in the DPRK remote IT-worker scheme. Most of what follows is transcribed from the cited post, in which a named researcher attributes these accounts to a single operator, Evan Jones. The attribution is theirs, not this site's.
The remainder was read by this site from the account itself and is cited to the page and date it was read.
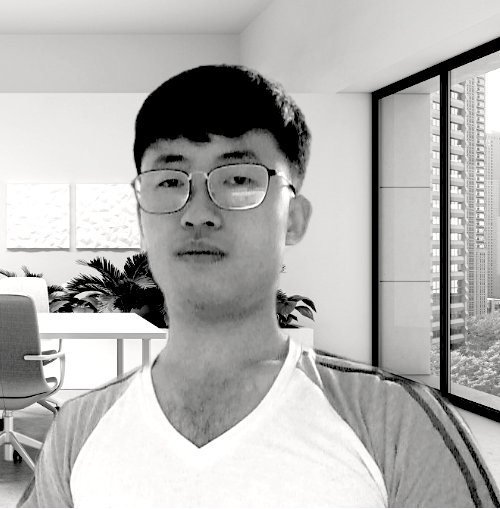
Portrait used by the persona.
Identifiers attributed to this persona
10 indicators the sources below record for this operator, each with its sources.
| Indicator | Type | Account status |
|---|---|---|
Evan Jones |
alias | |
Yucob Yun |
alias | |
evanj@d3vs.xyz |
email address | |
supertalented730@gmail.com |
email address | |
https://github.com/evanjonesxx |
github profile | live |
https://github.com/wenmoonx |
github profile | live |
https://gitlab.com/supertalented730 |
gitlab account | |
bip40 |
npm package | |
bitcoin-lib-js |
npm package | |
bitcoin-main-lib |
npm package |
Evan Jones
alias IT Worker Fraud CURATED
Sources
-
The post presents this identity as a friend of Aiden Mori. Three later citations fill the entry out. The commit comment thread on this account's own Ari-FE-Challenge repository is the operator writing in his own words: he gives supertalented730@gmail.com as his contact, describes himself as having built decentralised finance projects, automated market makers, a token launch platform, a sniping bot and a mixer, and names a token launch platform he says he worked on as a Solidity developer. The second commit is git metadata rather than prose and carries the same address as its author field, which is what ties the account to it without anyone having to take the persona's word for it; its merge message also records an SSH host alias named for the identity. The three npm packages are the same account publishing malware: reporting on NodeCordRAT names bitcoin-main-lib, bitcoin-lib-js and bip40 as uploaded by wenmoonx and taken down in November 2025. They are recorded as package indicators rather than held under the polarity rule because these are packages the operator published, not legitimate ones that were compromised, so the bare name identifies the threat rather than a victim. The post also states that the identity was itself targeted by the Marko Polo crew through a GitHub account that pushed malware. That account belongs to the party attacking this persona rather than to a DPRK operator, so it is not recorded as an indicator here; the approach it made is quoted in the held-back list, because the exchange is the clearest evidence of which direction the lure was running.
x.com/Narcass3/status/1941535948803801106 — Narcass3 (@Narcass3) -
Found on 18 September 2026 by taking the local part of an address this index already holds for this operator -- supertalented730 -- and asking GitLab whether an account exists under it. The address is on a consumer mail host, where the local part is a login the holder chose rather than one an employer assigned; handles taken from company addresses were excluded from this pass for that reason. The account states a display name of yucob yun. The login is what links this account to the rest; nothing here establishes that one person holds both, and a display name on a profile is a name the account presents, not an identification.
gitlab.com/supertalented730 — Chollima Hunter
Yucob Yun
alias IT Worker Fraud CURATED
Source
-
Found on 18 September 2026 by taking the local part of an address this index already holds for this operator -- supertalented730 -- and asking GitLab whether an account exists under it. The address is on a consumer mail host, where the local part is a login the holder chose rather than one an employer assigned; handles taken from company addresses were excluded from this pass for that reason. The account states a display name of yucob yun. The login is what links this account to the rest; nothing here establishes that one person holds both, and a display name on a profile is a name the account presents, not an identification.
gitlab.com/supertalented730 — Chollima Hunter
evanj@d3vs.xyz
email address IT Worker Fraud RESEARCHER POST
Source
-
The post presents this identity as a friend of Aiden Mori. Three later citations fill the entry out. The commit comment thread on this account's own Ari-FE-Challenge repository is the operator writing in his own words: he gives supertalented730@gmail.com as his contact, describes himself as having built decentralised finance projects, automated market makers, a token launch platform, a sniping bot and a mixer, and names a token launch platform he says he worked on as a Solidity developer. The second commit is git metadata rather than prose and carries the same address as its author field, which is what ties the account to it without anyone having to take the persona's word for it; its merge message also records an SSH host alias named for the identity. The three npm packages are the same account publishing malware: reporting on NodeCordRAT names bitcoin-main-lib, bitcoin-lib-js and bip40 as uploaded by wenmoonx and taken down in November 2025. They are recorded as package indicators rather than held under the polarity rule because these are packages the operator published, not legitimate ones that were compromised, so the bare name identifies the threat rather than a victim. The post also states that the identity was itself targeted by the Marko Polo crew through a GitHub account that pushed malware. That account belongs to the party attacking this persona rather than to a DPRK operator, so it is not recorded as an indicator here; the approach it made is quoted in the held-back list, because the exchange is the clearest evidence of which direction the lure was running.
x.com/Narcass3/status/1941535948803801106 — Narcass3 (@Narcass3)
supertalented730@gmail.com
email address IT Worker Fraud RESEARCHER POST
Source
-
The post presents this identity as a friend of Aiden Mori. Three later citations fill the entry out. The commit comment thread on this account's own Ari-FE-Challenge repository is the operator writing in his own words: he gives supertalented730@gmail.com as his contact, describes himself as having built decentralised finance projects, automated market makers, a token launch platform, a sniping bot and a mixer, and names a token launch platform he says he worked on as a Solidity developer. The second commit is git metadata rather than prose and carries the same address as its author field, which is what ties the account to it without anyone having to take the persona's word for it; its merge message also records an SSH host alias named for the identity. The three npm packages are the same account publishing malware: reporting on NodeCordRAT names bitcoin-main-lib, bitcoin-lib-js and bip40 as uploaded by wenmoonx and taken down in November 2025. They are recorded as package indicators rather than held under the polarity rule because these are packages the operator published, not legitimate ones that were compromised, so the bare name identifies the threat rather than a victim. The post also states that the identity was itself targeted by the Marko Polo crew through a GitHub account that pushed malware. That account belongs to the party attacking this persona rather than to a DPRK operator, so it is not recorded as an indicator here; the approach it made is quoted in the held-back list, because the exchange is the clearest evidence of which direction the lure was running.
x.com/Narcass3/status/1941535948803801106 — Narcass3 (@Narcass3)
https://github.com/evanjonesxx
github profile IT Worker Fraud RESEARCHER POST live
live
Source
-
The post presents this identity as a friend of Aiden Mori. Three later citations fill the entry out. The commit comment thread on this account's own Ari-FE-Challenge repository is the operator writing in his own words: he gives supertalented730@gmail.com as his contact, describes himself as having built decentralised finance projects, automated market makers, a token launch platform, a sniping bot and a mixer, and names a token launch platform he says he worked on as a Solidity developer. The second commit is git metadata rather than prose and carries the same address as its author field, which is what ties the account to it without anyone having to take the persona's word for it; its merge message also records an SSH host alias named for the identity. The three npm packages are the same account publishing malware: reporting on NodeCordRAT names bitcoin-main-lib, bitcoin-lib-js and bip40 as uploaded by wenmoonx and taken down in November 2025. They are recorded as package indicators rather than held under the polarity rule because these are packages the operator published, not legitimate ones that were compromised, so the bare name identifies the threat rather than a victim. The post also states that the identity was itself targeted by the Marko Polo crew through a GitHub account that pushed malware. That account belongs to the party attacking this persona rather than to a DPRK operator, so it is not recorded as an indicator here; the approach it made is quoted in the held-back list, because the exchange is the clearest evidence of which direction the lure was running.
x.com/Narcass3/status/1941535948803801106 — Narcass3 (@Narcass3)
https://github.com/wenmoonx
github profile IT Worker Fraud RESEARCHER POST live
live
Source
-
The post presents this identity as a friend of Aiden Mori. Three later citations fill the entry out. The commit comment thread on this account's own Ari-FE-Challenge repository is the operator writing in his own words: he gives supertalented730@gmail.com as his contact, describes himself as having built decentralised finance projects, automated market makers, a token launch platform, a sniping bot and a mixer, and names a token launch platform he says he worked on as a Solidity developer. The second commit is git metadata rather than prose and carries the same address as its author field, which is what ties the account to it without anyone having to take the persona's word for it; its merge message also records an SSH host alias named for the identity. The three npm packages are the same account publishing malware: reporting on NodeCordRAT names bitcoin-main-lib, bitcoin-lib-js and bip40 as uploaded by wenmoonx and taken down in November 2025. They are recorded as package indicators rather than held under the polarity rule because these are packages the operator published, not legitimate ones that were compromised, so the bare name identifies the threat rather than a victim. The post also states that the identity was itself targeted by the Marko Polo crew through a GitHub account that pushed malware. That account belongs to the party attacking this persona rather than to a DPRK operator, so it is not recorded as an indicator here; the approach it made is quoted in the held-back list, because the exchange is the clearest evidence of which direction the lure was running.
x.com/Narcass3/status/1941535948803801106 — Narcass3 (@Narcass3)
https://gitlab.com/supertalented730
gitlab account IT Worker Fraud CURATED
Source
-
Found on 18 September 2026 by taking the local part of an address this index already holds for this operator -- supertalented730 -- and asking GitLab whether an account exists under it. The address is on a consumer mail host, where the local part is a login the holder chose rather than one an employer assigned; handles taken from company addresses were excluded from this pass for that reason. The account states a display name of yucob yun. The login is what links this account to the rest; nothing here establishes that one person holds both, and a display name on a profile is a name the account presents, not an identification.
gitlab.com/supertalented730 — Chollima Hunter
bip40
npm package IT Worker Fraud RESEARCHER POST Taken down
OSV advisories
Source
-
The post presents this identity as a friend of Aiden Mori. Three later citations fill the entry out. The commit comment thread on this account's own Ari-FE-Challenge repository is the operator writing in his own words: he gives supertalented730@gmail.com as his contact, describes himself as having built decentralised finance projects, automated market makers, a token launch platform, a sniping bot and a mixer, and names a token launch platform he says he worked on as a Solidity developer. The second commit is git metadata rather than prose and carries the same address as its author field, which is what ties the account to it without anyone having to take the persona's word for it; its merge message also records an SSH host alias named for the identity. The three npm packages are the same account publishing malware: reporting on NodeCordRAT names bitcoin-main-lib, bitcoin-lib-js and bip40 as uploaded by wenmoonx and taken down in November 2025. They are recorded as package indicators rather than held under the polarity rule because these are packages the operator published, not legitimate ones that were compromised, so the bare name identifies the threat rather than a victim. The post also states that the identity was itself targeted by the Marko Polo crew through a GitHub account that pushed malware. That account belongs to the party attacking this persona rather than to a DPRK operator, so it is not recorded as an indicator here; the approach it made is quoted in the held-back list, because the exchange is the clearest evidence of which direction the lure was running.
thehackernews.com/2026/01/researchers-uncover-nodecordrat-hidden.html — The Hacker News
bitcoin-lib-js
npm package IT Worker Fraud RESEARCHER POST Taken down
OSV advisories
Source
-
The post presents this identity as a friend of Aiden Mori. Three later citations fill the entry out. The commit comment thread on this account's own Ari-FE-Challenge repository is the operator writing in his own words: he gives supertalented730@gmail.com as his contact, describes himself as having built decentralised finance projects, automated market makers, a token launch platform, a sniping bot and a mixer, and names a token launch platform he says he worked on as a Solidity developer. The second commit is git metadata rather than prose and carries the same address as its author field, which is what ties the account to it without anyone having to take the persona's word for it; its merge message also records an SSH host alias named for the identity. The three npm packages are the same account publishing malware: reporting on NodeCordRAT names bitcoin-main-lib, bitcoin-lib-js and bip40 as uploaded by wenmoonx and taken down in November 2025. They are recorded as package indicators rather than held under the polarity rule because these are packages the operator published, not legitimate ones that were compromised, so the bare name identifies the threat rather than a victim. The post also states that the identity was itself targeted by the Marko Polo crew through a GitHub account that pushed malware. That account belongs to the party attacking this persona rather than to a DPRK operator, so it is not recorded as an indicator here; the approach it made is quoted in the held-back list, because the exchange is the clearest evidence of which direction the lure was running.
thehackernews.com/2026/01/researchers-uncover-nodecordrat-hidden.html — The Hacker News
bitcoin-main-lib
npm package IT Worker Fraud RESEARCHER POST Taken down
OSV advisories
Source
-
The post presents this identity as a friend of Aiden Mori. Three later citations fill the entry out. The commit comment thread on this account's own Ari-FE-Challenge repository is the operator writing in his own words: he gives supertalented730@gmail.com as his contact, describes himself as having built decentralised finance projects, automated market makers, a token launch platform, a sniping bot and a mixer, and names a token launch platform he says he worked on as a Solidity developer. The second commit is git metadata rather than prose and carries the same address as its author field, which is what ties the account to it without anyone having to take the persona's word for it; its merge message also records an SSH host alias named for the identity. The three npm packages are the same account publishing malware: reporting on NodeCordRAT names bitcoin-main-lib, bitcoin-lib-js and bip40 as uploaded by wenmoonx and taken down in November 2025. They are recorded as package indicators rather than held under the polarity rule because these are packages the operator published, not legitimate ones that were compromised, so the bare name identifies the threat rather than a victim. The post also states that the identity was itself targeted by the Marko Polo crew through a GitHub account that pushed malware. That account belongs to the party attacking this persona rather than to a DPRK operator, so it is not recorded as an indicator here; the approach it made is quoted in the held-back list, because the exchange is the clearest evidence of which direction the lure was running.
thehackernews.com/2026/01/researchers-uncover-nodecordrat-hidden.html — The Hacker News
Sources
- x.com/Narcass3/status/1941535948803801106 — Narcass3 (@Narcass3)
- thehackernews.com/2026/01/researchers-uncover-nodecordrat-hidden.html — Narcass3 (@Narcass3)
- gitlab.com/supertalented730 — Chollima Hunter