
Brian Tonui
A fabricated professional identity used in the DPRK remote IT-worker scheme. Everything below is transcribed from the cited post, in which a named researcher attributes these accounts to a single operator, Brian Tonui. The attribution is theirs, not this site's.
Profiles and evidence
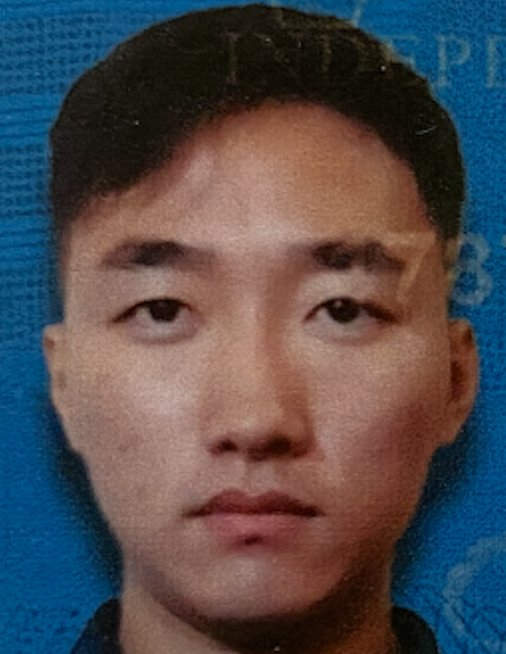
Portrait of the persona, from an identity document.
Identifiers attributed to this persona
1 indicator the source attributes to this operator, each with its sources.
| Indicator | Type | Account status |
|---|---|---|
Brian Tonui |
alias |
Brian Tonui
alias IT Worker Fraud RESEARCHER POST
Source
-
The opening post of the DRC Team thread describes this identity as an IT worker who built KYC and AML systems at an exchange, worked at Funnull with administrative access, used the GitHub account associated with the Polyfill supply-chain attack, and used the services of Serbian laptop farmers.
x.com/narcass3/status/2074856020048838964 — Narcass3 (@Narcass3)
Sources
- x.com/narcass3/status/2074856020048838964 — Narcass3 (@Narcass3)